


 New |
Sail numbers |  Блоги |  Фотографии |
Правила | Календарь соревнований | Пользователи |
 |
|
|
|||||||
| Начало | Что нового? | Новые изображения | Загрузить | Поиск |
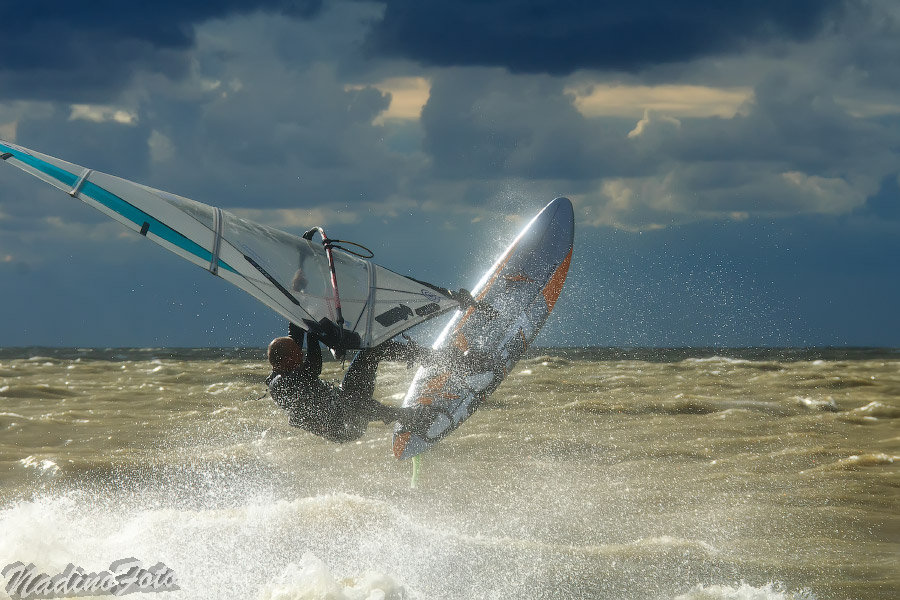
| Должанка 2013 Фотографии с каталок на Должанке в 2013 году |
| Сергей Чижов 6 сентября | Опции изображения |
|
 Диафильм |
 |
 › |
 ›› |
 09.09.2013 20:04 |
| Раздел: | Фотогалерея RaceYou! › Фотографии сообщества RaceYou! › Каталки! › Должанка 2013 | ||
| Описание: | Запад-юго-запад на Азове | ||
| Автор: | AlexSilver (Просмотреть все изображения от AlexSilver) | Разрешение: | 900 x 600 |
| Просмотров: | 20,057 | Размер файла: | 155.7 Кб |
| Комментариев: | 2 | Ключевые слова: | нет |
|
|
| Комментарии для изображения: Сергей Чижов 6 сентября |
|
11.01.2026, 08:25
|
#1
|
|
Windsurfer |
Hi everyone. Site on 1C-Bitrix, for the third month in a row every night there’s heavy brute-force on /bitrix/admin/ and managers’ login pages. Thousands of login/password combinations per minute, mostly from old leaks + dictionary attacks. Already set up fail2ban, IP limits, Cloudflare WAF with managed rules, reCAPTCHA on admin — still 5–10 accounts get compromised per month, have to force everyone to change passwords and enable 2FA manually. Has anyone actually defeated these nightly admin attacks without making life miserable for your own staff?
|


|
|
11.01.2026, 10:02
|
#2
|
|
Windsurfer |
I had exactly the same issue on a corporate portal (also Bitrix + custom CRM), in August–September we almost lost several sales managers’ accounts. Standard protections (WAF, rate-limits, CF Turnstile) only stopped dumb bots, while “smart” ones with proxy rotation and human-like behavior succeeded in 10–15% of cases.
In October I installed http://xcaptcha.com/ specifically on all admin login forms and employee personal cabinets. Set the strictest mode just for this area (left public part lighter). In 3 months — zero successful brutes, even though logs still show 15–25 thousand attempts per night. Real employees in 98.7% of cases see absolutely nothing — only two people had a minimal challenge appear (one was using TOR, the other tried 8 times in a row with wrong passwords). Brute-force load on the server dropped almost to zero, now I sleep peacefully at night again. Very convenient that you can set different protection levels for different site paths. Highly recommend, especially if your admin panel is exposed to the internet. |
|
|
